One clinic can never see another's patients
Every patient row belongs to a clinic, and the clinic always comes from the logged-in user, never from the request. A test logs in as clinic B and tries clinic A's patients; it must get "not found".
Case study · Health data
An EMR for solo and small family medicine clinics in the Philippines. Health data is sensitive personal information under the Data Privacy Act (RA 10173), so every design decision starts from one rule: patient-data safety beats speed.
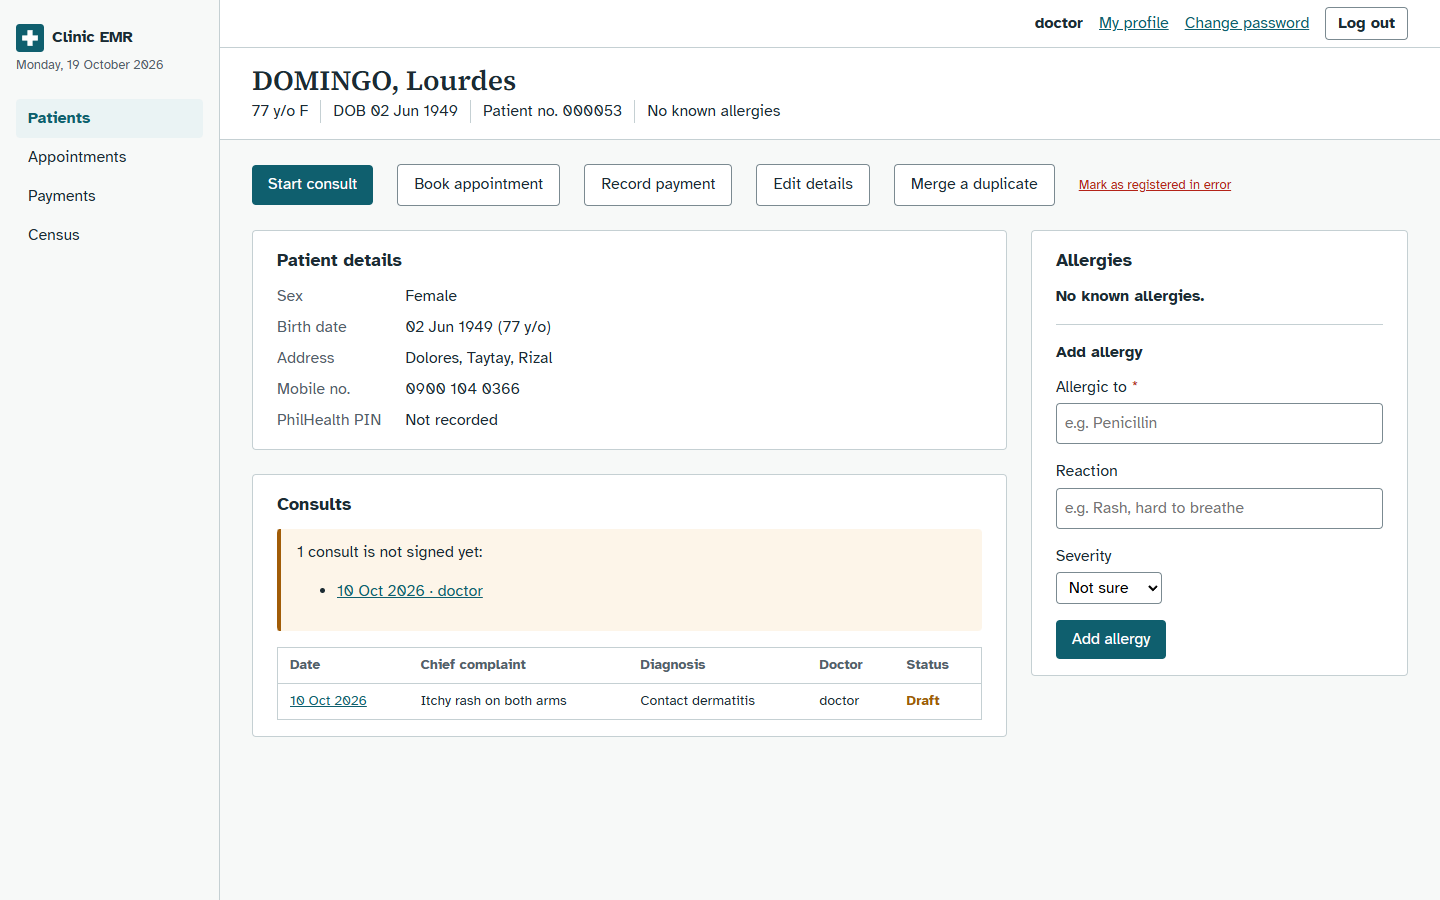
A small family clinic needs a handful of things done well: find the right patient quickly, write the consult, and print a prescription or medical certificate that a pharmacy or an employer will accept. Systems built for hospitals are too big for that. A clinic system also can't cut corners on privacy, because one leaked chart is a breach under the law.
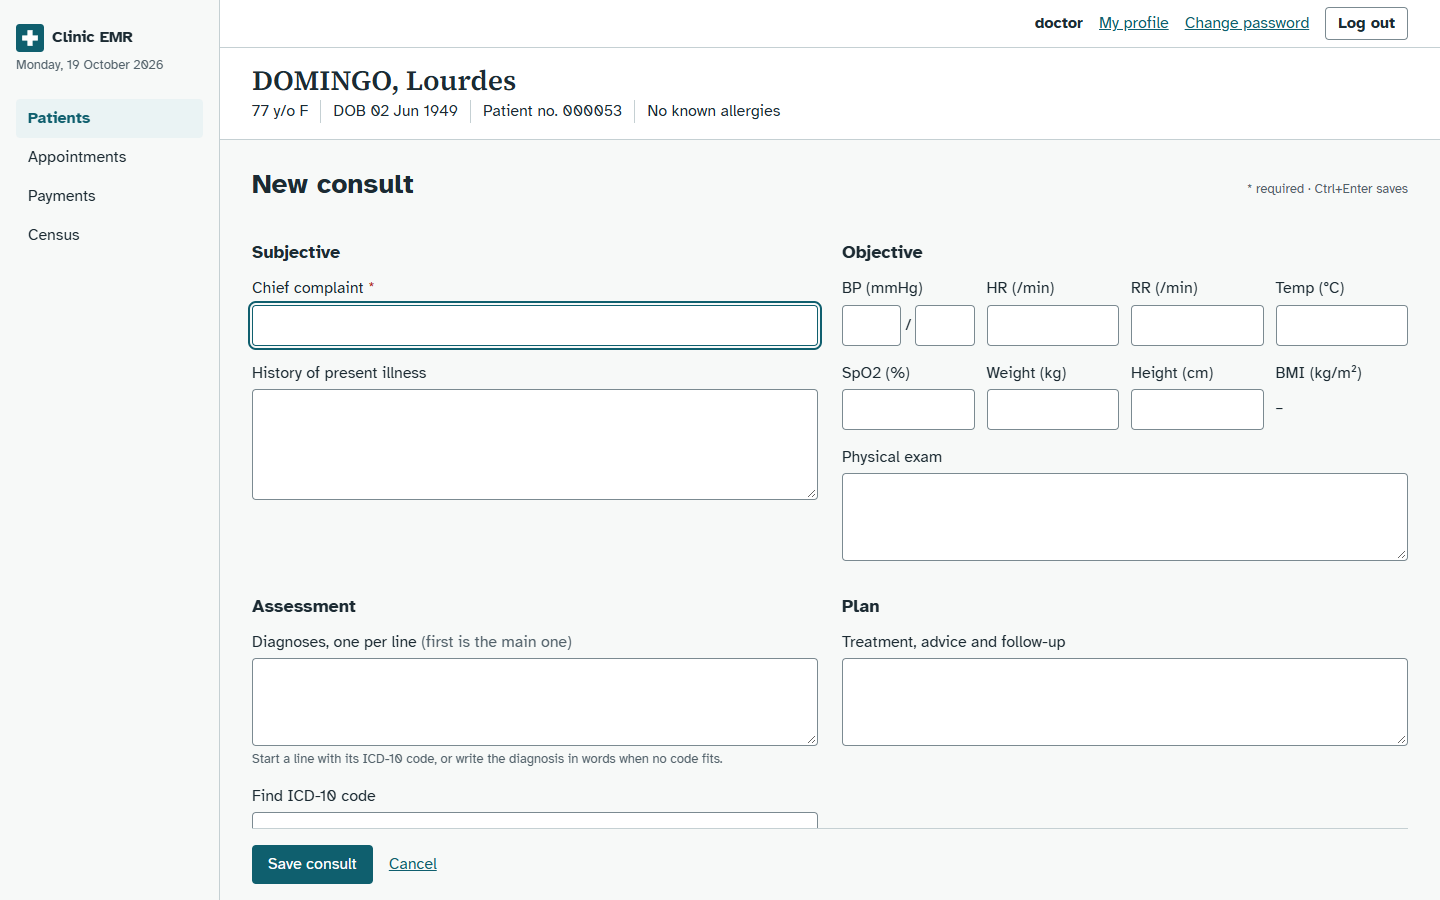
Every patient row belongs to a clinic, and the clinic always comes from the logged-in user, never from the request. A test logs in as clinic B and tries clinic A's patients; it must get "not found".
The app connects with a database login that can read and add rows but can't delete them or change the audit tables. Migrations run in a separate step as the owner, so even a SQL injection bug can't wipe the record.
Doctors and admins use an authenticator app. The popular Java TOTP libraries hadn't had a release since 2020, so I wrote the check in about 60 lines of plain JDK code and tested it against the official RFC 6238 test vectors.
Browser printing adds headers and margins that differ on every PC. The server makes the PDF at the clinic's paper size, so it prints the same everywhere, and every print is logged.
I build this project with Claude Code. The repository holds the rules the agent must follow (patient-data safety, coding standards, testing, database changes), and the agent doesn't decide clinical behavior: unclear medical or product questions come back to me and the doctor. The checks below apply to every change, whoever wrote it.
One server in AWS Singapore with an encrypted disk, no open SSH port (Session Manager instead), HTTPS through Caddy, and deploys from GitHub Actions. A copy with fake data runs behind Cloudflare Access for testing.
I build systems where the data has to stay safe, and I'm open to full-time roles.
Email me Next: Security Operations Manager →